Industry executives and experts share their predictions for 2025. Read them in this 17th annual VMblog.com series exclusive.
By Mark Logan, CEO of One Identity
With 2025 approaching, artificial intelligence (AI) continues to generate significant shifts in the cybersecurity landscape. As AI becomes increasingly integrated across industries, organizations must prepare for the reality that their data, systems, and users are increasingly exposed to risks that are not fully understood. The widespread adoption of generative AI introduces ongoing and complex vulnerabilities – and leaders must think critically about reshaping both their defensive and offensive security strategies.
Here are three predictions that organizations will have to prepare for in 2025:
Organizations will have to treat AI like another colleague
AI applications are deeply embedded in today’s business operations, and this integration makes them high-value targets for cybercriminals. In 2025, hackers will not only breach AI applications but also manipulate the AI in ways that could disrupt business processes or cause large financial losses. Organizations will need to start treating an AI application like a person, much in the same way as we did for bots not too long ago. It will now be essential for organizations to implement sophisticated monitoring, response systems, and security protocols specifically tailored for AI. Additionally, proactive employee training and threat intelligence sharing will become critical components of a robust security strategy.
Generative AI will increase the risk of non-human identities (NHIs)
Generative AI is rapidly multiplying the presence of NHIs within organizations – and 2025 will see this trend increase. The unmanaged proliferation of NHIs – especially as organizations rush to adopt generative AI solutions – opens new avenues for attackers and increases the complexity of identity management. With the hysteria around AI (and the generally unmanaged proliferation of genAI), the danger of non-human identities in 2025 will rise. As AI continues to automate work, NHIs will require dedicated identity management practices. Security teams must extend identity and access management protocols to NHIs, applying principles like least privilege, regular auditing, and real-time monitoring for autonomous agents. Without these precautions, NHIs could quickly become an organization’s weakest link.
There will be a spike in cyber insurance premiums with the use of AI
Current security concerns from the use of AI and other ongoing transformative efforts will spike cyber insurance premiums. Insurers are watching AI closely as the potential for AI-driven incidents – including breaches, fraud, and system failures – forces a reevaluation of risk assessments. As companies implement AI in more of their organizational processes, insurers will have to recalculate risks and factor in the potential impact of AI-driven incidents. Now, organizations that lack the demonstration of AI governance and cybersecurity diligence may face increased insurance costs. This pressure will drive companies to enhance their risk management practices, investing more in preventive measures to control rising premiums. This will drive a new era of AI risk management where companies treat AI vulnerabilities as seriously as traditional threats. They also need to understand that premium hikes aren’t just financial inconveniences – they’re indicators of a risk landscape transforming in real time.
AI will again have an integral role in cybersecurity – posing as a more transformative and challenging factor. Companies must secure AI applications as if they are humans, protect NHIs, and prepare for rising cyber insurance costs. Organizations that take proactive steps in managing AI risks will be better positioned to harness AI’s potential without falling victim to its risks. Building a culture of cybersecurity awareness among employees and implementing robust training programs will become essential to organizational success. As cyber threats evolve, ensuring comprehensive protection for data and systems while encouraging collaboration across the industry will ultimately play a critical role in overall security resilience.
##
ABOUT THE AUTHOR
Mark Logan, CEO of One Identity
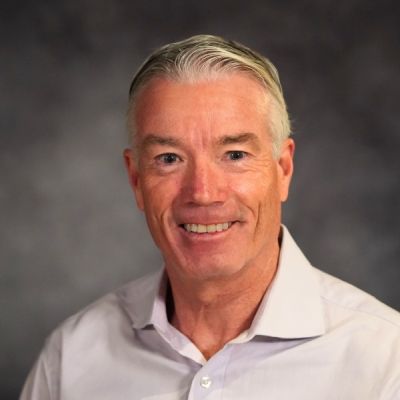
Mark Logan serves as Chief Executive Officer of One Identity and joined the company in June 2022. He is responsible for driving the overall growth strategy, go-to-market and P&L for One Identity. Mark is a seasoned executive with experience developing enterprise software companies to achieve successful growth. He is a proven leader with nearly two decades of C-suite experience at companies such as Emptoris (now part of IBM), Attunity, and most recently LogRhythm. Having been in the cyber security space for several years, Mark believes One Identity is in the right market at the right time to provide critically important cybersecurity protection for enterprises, public sector organizations and federal agencies.