Industry executives and experts share their predictions for 2023. Read them in this 15th annual VMblog.com series exclusive.
The State of Cybersecurity: What to Anticipate in 2023 Predictions
Five threat outlook predictions and what they will mean for businesses in the year ahead.
By Jeff Costlow, CISO of ExtraHop
The threat landscape is seemingly growing more sophisticated by the day, and traditional defensive tactics are clearly no longer cutting it. Between advanced threats and volatile geopolitics, security teams have their hands full.
As we head into 2023, the digital battlefield is going to shift. Some of these shifts will be expected – and ideally, prepared for – and others are the result of a new and changing global economy. Let’s take a look at some of the most important cybersecurity themes that IT, security and cloud operations teams need to know next year.
1. Nation state actors will go all-in on credential stuffing
In March of 2022, it’s safe to say no one would have expected the Russia Ukraine war would still be raging come November. Experts warned of the cyber implications that would undoubtedly rain down upon any business that took a stance, but the other shoe seemingly didn’t drop. While breach attempts set new records quarterly, there wasn’t one standalone cyber incident that stands out. Entering 2023, depending on the state of the physical war, I would expect the digital war to really begin.
Former Soviet Bloc countries are second-guessing Russia’s military acumen and security support. This means they’re looking to other countries for cybersecurity alignment, including China. The realignment of physical support will coincide with a similar adjustment in the cybersecurity world and companies may see different nation-state campaigns as Russia loses some of its cyber-controlled territories.
While not a new tactic, nation state actors will escalate their attempts at credential stuffing, particularly to be used against firms taking opposing stances on conflict. Usernames and passwords for personal social media accounts continue to make up a large portion of breached data dumps, so 2023 will most likely see a rise in more targeted account takeover attempts with leaked credentials – especially lucrative corporate accounts. For example, my teams noticed an uptick in unauthorized access attempts and trolling on our own corporate accounts when the company shared resources related to CISA’s Shields Up guidance.
2. New regulations in effect will drive increased adoption of new tech
We’ll undoubtedly continue to see more data privacy legislation passed on both the state and federal levels. California led the way with CCPA, and on January 1, the expanded amendment CPRA, comes into effect. In addition to state-level legislation, Congress has proposed new national privacy legislation and policies. This movement is beginning to pick up support and momentum nationwide, and a split Congress looking for mutual wins may make it a priority next year.
With privacy being made a priority by world leaders, industry support for Fast Identity Online (FIDO) authentication and Apple’s new passkey capability in iOS16 could see good adoption in the coming year. This would limit the efficacy of account takeovers through phishing and password guessing/ reuse. As a result, attackers will be forced to focus on other means for initial access, like zero days and supply chain attacks, that focus more on company-wide workloads and less on specific users – but more on this in a bit.
3. All eyes on post-breach protocols
While cyberattacks continue to get more sophisticated, the entry points have largely remained the same. Research tells us that enterprises are still using insecure and outdated protocols that provide easy access points for attackers. Despite increased funding for cyber defense tools, we will continue to see these types of attacks if businesses continue to leave their front door wide open.
We will also continue to see attackers use non-traditional techniques to breach system perimeters, such as leveraging legitimate VPN credentials as we saw in the big Uber hack of 2022. It will be essential for organizations to invest in post-breach defenses and processes that mine their own data to correlate new IoCs and threat intelligence information for defensive and remediation purposes.
4. More businesses will embrace open frameworks to effectively implement new tools
The days of software potential are long gone. With so many tools available, implementation must be effective, quickly.
For example, more businesses are leaning on MDR providers to enable XDR as it ensures they get the best retained talent to monitor their networks on a daily basis. The promise of XDR is clear – contextualized, coordinated data helps teams streamline, prioritize, and automate work. However, the roadmap to actually get there continues to be a challenge for organizations.
In 2023, we will see more vendors embracing open frameworks to assist in the actual implementation of XDR that works for each bespoke organization. The industry has struggled with a one-size-fits-all approach to XDR, so 2023 will bring about more integrations, options and, hopefully, adoption.
5. Budget allocation becomes the most important part of security programs
As tool fatigue and inflation mingle with a decline in the reputation cost for breached companies, it’s a possibility that cybersecurity spending will be curtailed. Rather than bump or cut to budgets, I urge leaders to take a closer look at where the budget is being placed.
Spending on perimeter network defense still out paces spending on post defense strategies. The consequences of this imbalance in spending is that attackers are finding very easy ways to bypass all these network defense tools and, once inside the environment, they have their run of the place.
The current network defense spending trend is based on an assumption of how attackers attack and is outdated. In 2023, organizations will need to adapt to these changes and shift their spending allocation to combat today’s attack methodology.
As high-profile attacks grip the news cycle, security is no longer exclusively the “headache” of the IT department. It’s everyone’s problem. The proliferation of advanced attacks in 2022 laid the groundwork for a number of industry shifts in 2023. With external elements like the economic downturn and global conflict in play, business leaders need to be strategic in where to place their budgets and which types of tools to invest in to do more with less.
##
ABOUT THE AUTHOR
Jeff Costlow, CISO at ExtraHop
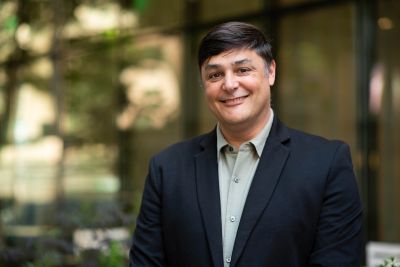
As a security technologist and leader for over 20 years, Jeff’s deep experience securing information and technology assets as well as years of successful engineering leadership have resulted in secure product deployments to thousands of customers.
As the CISO at ExtraHop, Jeff leads the ExtraHop team towards groundbreaking security and privacy services in ExtraHop’s best of breed network detection and response tool.