Industry executives and experts share their predictions for 2022. Read them in this 14th annual VMblog.com series exclusive.
A Rapidly Expanding Cloud Attack Surface and Supply Chain Threats Will Loom Large for Enterprises
By Fabian Yamaguchi, Chief Scientist at ShiftLeft Inc.
In 2022, organizations will increasingly turn to cloud deployments and supply chain partnerships to boost operational efficacy, business-benefiting outcomes and competitive edge: Spending on business process as a service, infrastructure as a service, software as a service and other cloud offerings is expected to surpass $482 billion next year, up from about $396 billion this year, according to Gartner.
Meanwhile, the market for supply chain management is projected to reach more than $52.6 billion in 2030 – up from just under $18.7 billion in 2020 – driven by greater demand for industrial-grade digital technology, cloud-based supply chain management software and improved supply chain visibility, according to Allied Market Research.
With the growth, however, come new opportunities for attacks. These opportunities lead our predictions for the upcoming year, followed by additional observations about trends in fuzz testing, security “un-solutions,” buyouts, programming languages and security education:
The expanding cloud attack surface will force organizations to step up
The safeguarding of cloud deployments is actually still in its infancy, and we will see more traction here. In 2022, we will most likely focus on rapidly identifying the attack surface exposed by these applications, as well as hidden entry points.
Yet, it will become clear that cloud providers only offer the platforms, but not the necessary means to use them securely. This will remove any ambiguity over responsibilities: Organizations and developers using cloud infrastructure will oversee security directly and/or employ third-party tools and services.
Supply chain attacks will reveal more inadequacies of current tools
Given the consequences of abundant supply chain attacks, organizations will realize that software composition analysis offerings provided today cannot sufficiently address the problem. Despite this, when breaches become public, many vendors in the space will nonetheless declare that their offering could have prevented the breach.
Fuzz Testing will tilt toward finding Web-application vulnerabilities
Fuzz testing – a quality-assurance technique used primarily to discover memory corruption flaws – has always been about vulnerabilities. In 2022, we should see more fuzz testing for vulnerability identification in memory safe languages used on the Web instead.
Misconceptions about security tools will grow – as will the popularity of inadequate, simplistic “un-solutions”
Computer science illiteracy will increase, making it even harder to communicate which security processes can and cannot be automated for customers. Subsequently, many organizations will flock to solutions that are simple (i.e. easy to comprehend) but ineffective while avoiding those designed and built to be comprehensive and effective – but are complex. As a result, too many companies will miss out on tools they really need – those which deliver true value and benefits.
More in play: Rust and Go will ascend – but memory corruption flaws will remain relevant
On the programming language side, both Rust and Go will gain more traction while new C/C++ will not substantially decrease. In effect, memory corruption flaws will remain relevant in 2022.
Security education: We’ll see a “wild wild West” both good and bad
We’ll continue to seek out education about security, but the quality of content offerings will vary drastically. On the downside: We will see more “get rich quick” scams in education, especially in the “bug bounty” space.
Conclusion
Our takeaways essentially come down to this: In 2022, enterprise security leaders will better position themselves through careful discrimination, productive skepticism, the demanding comparison of competing products and the full-bore rejection of marketing hype. The devil will be in the details. Or, as some say, if you skim over the details, you may meet up with the devil at a high cost to your organization. Choosing well and insisting on informed decisions will reap the benefits of getting it right in 2022.
##
ABOUT THE AUTHOR
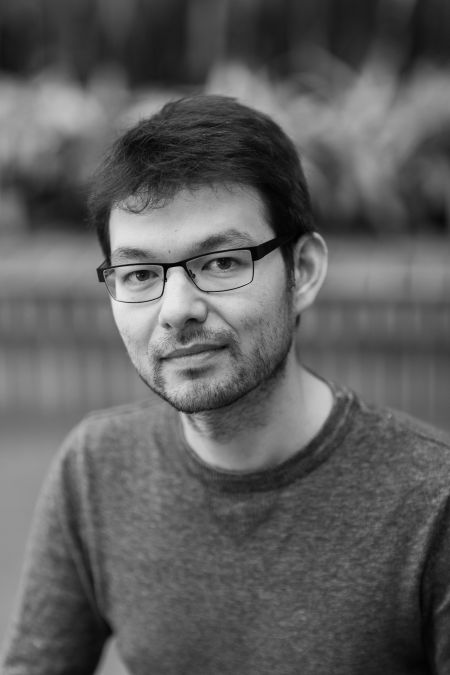
Fabian Yamaguchi is Chief Scientist at ShiftLeft Inc and an Associate Professor Extraordinary at Stellenbosch University. He has over 15 years of experience in the security domain, where he has worked as a security consultant and researcher, focusing on manual and automated vulnerability discovery.