By Dimitris Vassilopoulos, Solutions Architect, Upwind Security
Cloud native security sneaks into war stories about broken pipelines, late-night incidents and AI experiments. People are tired of endless ‘critical’ issues and want to focus on what is actually risky in production, right now.
From “what’s configured” to “what’s really happening”
Most of us started in cybersecurity by scanning things: networks, servers, web applications and then cloud accounts, Kubernetes manifests and container images. In slower, more static environments, that approach made sense; you could assume that what was configured was more or less what was running.
In a typical cloud native stack, that assumption falls apart. Workloads are ephemeral, teams ship changes constantly and Kubernetes operators, service meshes and controllers keep reconciling desired state with whatever the cluster is doing at the moment. Add AI agents that trigger workflows and make API calls on their own, and you get systems whose behavior changes faster than traditional tools can refresh their inventory.
CI and infrastructure-as-code checks are still essential, but more people now want something that says, “Here’s what your workloads are actually doing right now, and why it matters.”
Less alert fatigue, more actionable insights
Ask any platform, SRE or security engineer about alerts and you will probably get a sigh and a story. Dashboards are full, Slack channels are noisy and the backlog of “we should fix this someday” tickets keeps growing. At some point, the problem isn’t visibility; it is triage.
A runtime-aware view of cloud native security tries to fix that by lining up with the questions people actually ask in incident reviews and design docs, such as:
- Is this workload exposed to the internet and actually receiving traffic right now?
- Is that scary-looking CVE buried in a library that never loads, or in a function sitting in memory on a busy service?
- Does this pod talk to sensitive data stores or run with a highly privileged identity?
- Why is this service suddenly sending egress traffic to a generative AI endpoint or to some unpatched legacy system?
Once you connect those dots, your list of “things to care about this week” usually shrinks dramatically. The conversation shifts from “look how many alerts we raised” to “here are the few actionable issues that combine real exposure, real impact and real exploitability.”
How this lands for DevOps, SREs and SecOps
Listen to enough hallway conversations and you notice how shared this problem feels. DevOps and platform engineers, SREs and security teams are all drowning in slightly different versions of the same noise.
Runtime-aware, cloud native-friendly approaches aim to give each group something useful from the same underlying context:
- DevOps and platform teams can cut out “theoretical” issues and fail builds only when a vulnerability or misconfiguration is likely to be exploitable in production, linking each issue to a service, repo or pipeline.
- SREs get speed during incidents: a single place to see traffic flows, recent changes and odd workload behavior, so “What changed?” is easier to answer.
- SecOps can focus threat detection on what is really exposed and behaving strangely, not every possible attack path, and tell a clear story from cloud asset and identity down to pod processes and API calls.
When all three groups share the same picture, handoffs start to feel less painful. You are no longer translating between three versions of reality; you are arguing about priorities on top of the same set of facts.
A grounded view of where this is going
Zooming out, this isn’t about inventing a new buzzword. It is about catching our security habits up to the way cloud native systems already behave. Cloud native workloads including the rise of AI agents have all pushed us toward environments that are fast, ephemeral and heavily automated. A configuration-only view just doesn’t keep up anymore.
If you are responsible for these systems day to day, a few practical moves are worth considering:
- Treat runtime as a first-class signal alongside IaC and image scanning.
- Measure and actively reduce alert fatigue; that is a people and reliability problem, not just a security one.
- Lean on vendor-neutral building blocks so different teams can plug into the same foundation instead of each buying their own silo.
- Use AI to help comb through data and connect dots, but keep humans in charge of judgement calls and risky automation.
The cloud native realm has always rewarded teams that accept reality and design for it instead of wishing things were simpler. Runtime-aware cloud security is just the latest example of that mindset:
Less time worrying about every possible issue on paper, more time fixing the few risks that genuinely matter in production.
A quick personal lens
For me, this shift has been building for years. I’ve come to the cloud native world from a long way back-traditional networking and security, managed security services, offensive cloud security-and, more recently, through the long grind of earning Golden Kubestronaut status across CNCF and Kubernetes certifications.
The biggest lesson hasn’t been a single exam objective or a clever attack path; it is how far real production systems drift from the neat diagrams we use to explain them.
The closer you get to what is actually running, the easier it becomes to cut through the noise and have honest conversations about risk with the teams who own the workloads.
##
KubeCon + CloudNativeCon EU 2026 is taking place in Amsterdam, the Netherlands, from March 23-26. Register now.
ABOUT THE AUTHOR
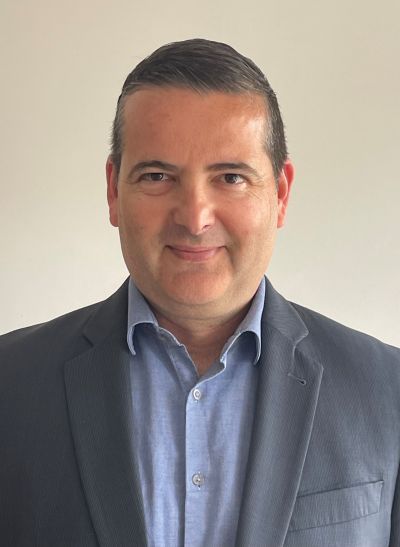
Dimitris is a passionate cloud-native security solutions architect and the first Greek Golden Kubestronaut, focused on securing cloud-native ecosystems, driving secure DevOps, and empowering businesses to innovate safely and confidently in the cloud, at scale.