OX Security announced the next iteration of their solution with the first ever Active ASPM Platform. Incorporating active analysis in an ASPM solution marks a critical step forward for AppSec by delivering a proactive and converged solution that moves beyond the limitations of existing solutions on the market.
By unifying AppSec practices with comprehensive visibility and traceability, contextual prioritization, and automated, no-code workflow-driven response, this “active” approach facilitates the continuous and accurate targeting of critical threats, significantly reducing alert fatigue. Recognized as a Gartner Cool Vendor, OX Security is setting new standards in addressing the pressing needs of the market. OX Active ASPM empowers development and security teams to deliver secure applications while significantly reducing operational friction.
“We’ve spoken with hundreds of security and development teams, and it’s clear they are drowning in manual AppSec tasks and struggling to balance development speed with ensuring secure releases. Our vision is to empower organizations with a solution that addresses these current application security needs and anticipates future challenges,” stated Neatsun Ziv, CEO and Co-Founder of OX Security. “The OX Active ASPM Platform is a testament to this commitment and our mission to eliminate manual AppSec practices. With its advanced data collection abilities and seamless no-code automation, our platform is engineered to scale alongside organizations, adapting to their goals and growth.”
OX Active ASPM also helps organizations keep pace with an ever-changing regulatory environment by providing a dynamic software lineage list that aligns with emerging standards like the EU Cybersecurity Act, CISA, and NIST Cybersecurity Framework. This proactive adaptability to global regulations ensures organizations are prepared for today’s demands and future regulatory shifts.
Key features and capabilities of OX’s Active ASPM include:
- Continuous End-to-End Coverage: OX’s native scanners seamlessly integrate with the user’s source control, CI/CD, registry, and cloud environments, providing users with comprehensive visibility, traceability, and actionable insights, reducing the need for manual oversight and analysis and eliminating the need for multiple tools that may result in coverage gaps and technical debt.
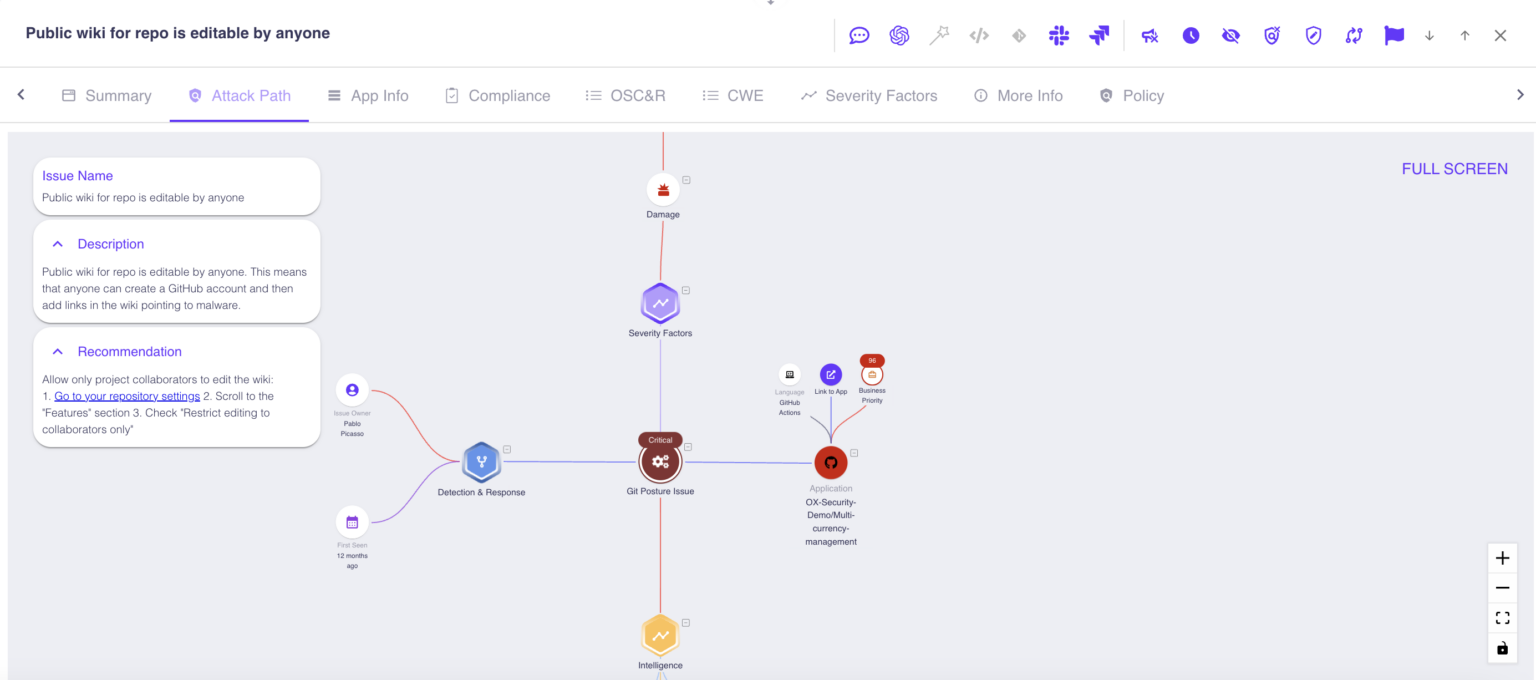
- Attack Path Analysis: Comprehensive attack path analysis enables users to visualize and quickly address security concerns from a single screen, significantly speeding up response time and improving efficiency in managing security tasks.
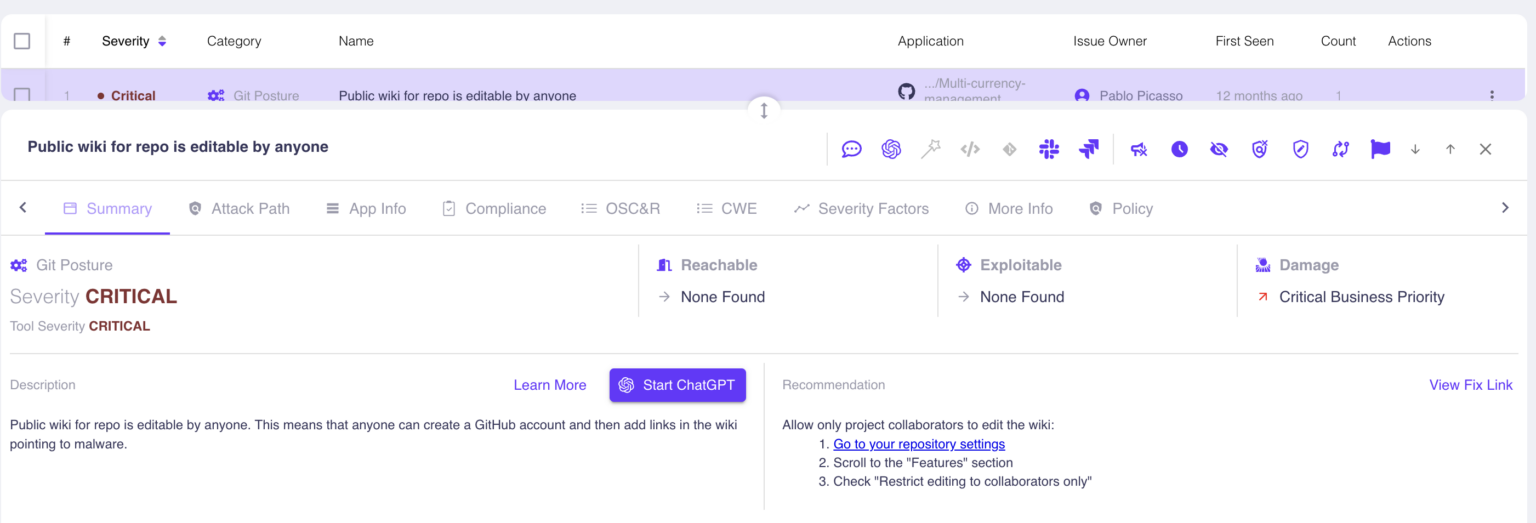
- Active Context Analysis: OX utilizes a 3-layer model to evaluate threats beyond the surface level, incorporating environmental, business, and threat considerations. It effectively assesses vulnerability, exploitability, reachability, and business impact, reducing noise by over 95%. The analysis offers comprehensive Dockerfile insights, including SBOM and SCA for various components. OX uniquely identifies plaintext secrets in code, containers, and logs, providing context on each finding’s impact. It also includes detailed open-source security analysis, advanced taint analysis, and data flow tracking to secure the SDLC against vulnerabilities proactively.
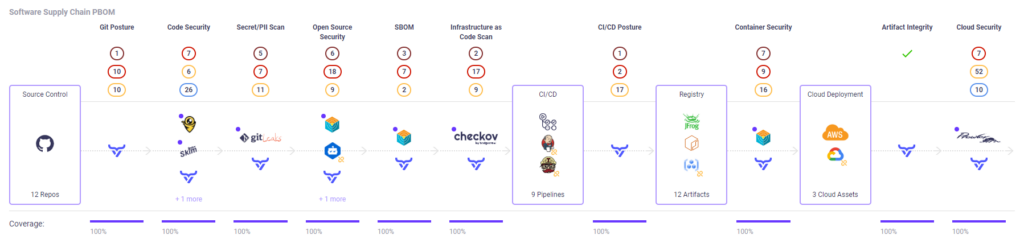
- Pipeline Bill of Materials (PBOM): OX’s proprietary PBOM ensures greater software integrity and minimizes attack surfaces. Going beyond the capabilities of a standard SBOM, a PBOM acts as a dynamic inventory, encompassing every aspect of software development. It provides a real-time list of software lineage, tracing each phase from code inception to release and pinpointing vulnerabilities. Thorough tracking enhances transparency and trust and empowers teams with crucial insights, enabling them to address vulnerabilities and maintain compliance standards preemptively.
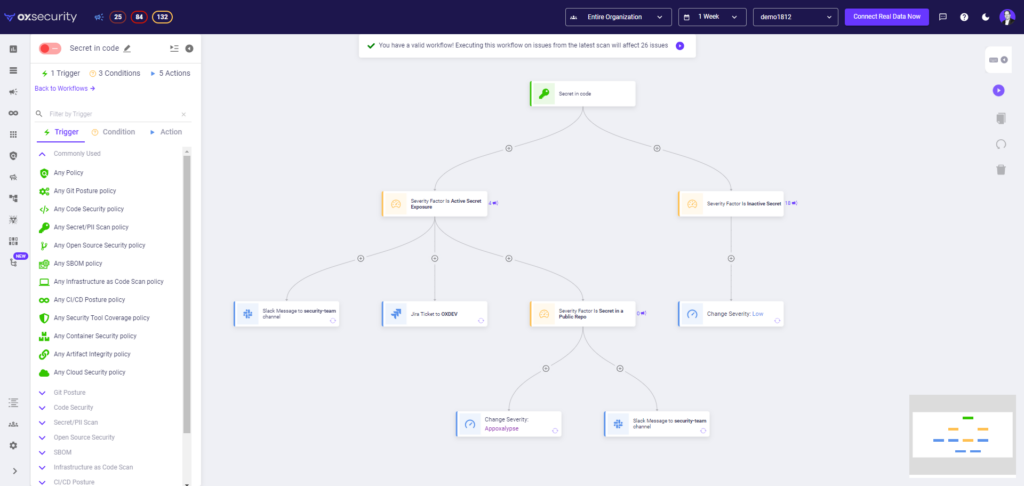
- No-Code Workflow Automation: A simple drag-and-drop interface simplifies the creation of tailored remediation and response workflows, significantly reducing manual tasks by automating ticketing and notifications and enforcing granular policies to prevent security issues from reaching production. By automating these processes without needing custom code, OX simplifies the creation of custom workflows and enhances security by preventing lapses in production, leading to quicker version releases and a more efficient, secure development environment.
“The OX Active ASPM Platform is a game-changer in AppSec,” said Hadass Harel Lavie, security architecture manager at eToro. “It has enhanced our security posture and streamlined our secure development process, allowing us to seamlessly embed security into our development lifecycle. This provides a full spectrum at one glance and focuses us on the essence by validating and prioritizing findings based on the attack path anatomy.”