By Michael Olechna, Mobile App Security Evangelist, Guardsquare
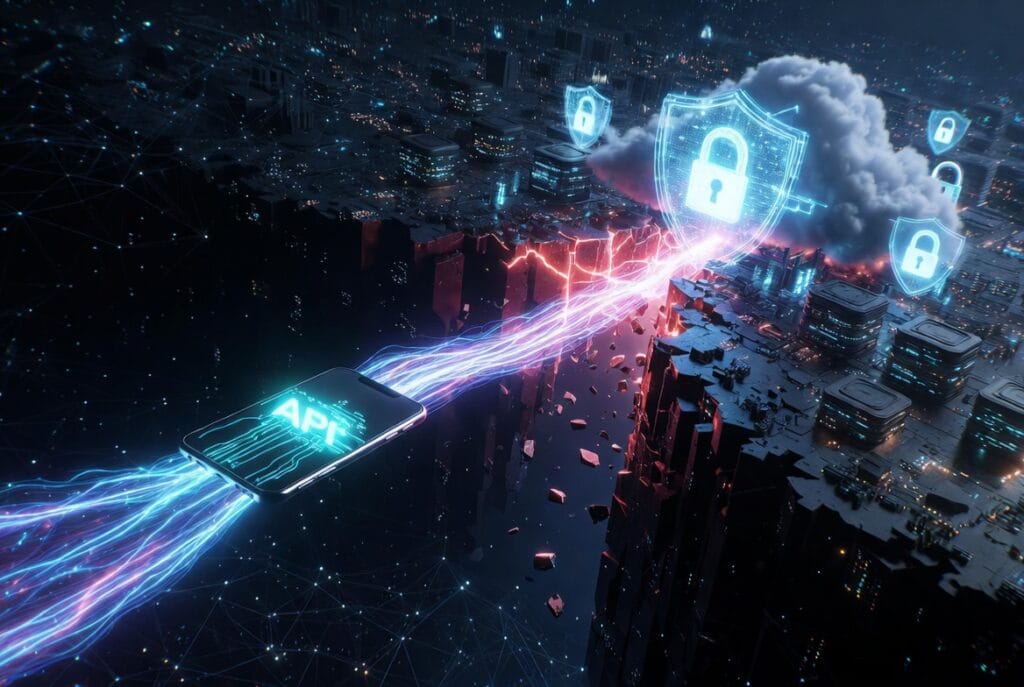
Enterprise security teams spend enormous effort securing cloud infrastructure, APIs, and backend systems. Yet many still overlook a critical question. Can the mobile app making those API calls actually be trusted?
That question matters because the mobile app is now one of the most important entry points into enterprise systems. It connects users to accounts, payments, loyalty programs, healthcare data, streaming content, and other high-value services. The API may be protected by mature cloud security controls, but the mobile client operates in an environment the enterprise does not fully control.
That creates a trust gap between the backend and the app.
Many teams assume that if a request appears to come from the legitimate app, it can be trusted. The request may use application-embedded secrets, travel over TLS, and follow the expected structure of normal traffic. But attackers have several ways to challenge those assumptions.
Common threats include:
- Traffic interception, where attackers proxy communications between the app and the backend
- Static secret extraction, where embedded keys or credentials are pulled from the app binary
- App modification, where attackers alter app behavior through tampering or hooking
- Compromised devices, including rooted or jailbroken devices, that weaken trust assumptions
- Bot farms, where attackers automate actions through real devices, emulators, or headless scripts
For cloud and security teams, the issue is not only whether the API is encrypted. It is whether the backend can determine that the request came from a genuine, untampered app running in a trusted environment.
Understanding the Attack Paths
A man-in-the-middle (MITM) attack places the attacker between the app and the backend server. The attacker intercepts traffic, presents a fraudulent certificate, and attempts to decrypt or modify requests before forwarding them to the legitimate backend. TLS helps protect against passive eavesdropping, but it does not automatically prove that the client itself is legitimate.
A man-at-the-end (MATE) attack targets the application instead of the communication channel. In this scenario, the attacker reverse-engineers, instruments, or tampers with the app to observe secrets, modify logic, or manipulate requests before they are sent. This is where traditional network controls may not be enough, because the request can appear valid by the time it reaches the backend.
Bot farms create another challenge. Device-based bot farms use real devices or emulators to automate actions in the app. Headless bot farms go further by directly mimicking API requests, often after the communication layer has been reverse-engineered. These attacks can support credential stuffing, scraping, fraud, promo abuse, content abuse, account takeover, and other forms of automated misuse.
Comparing Common Defenses
TLS is essential, but it only protects the communication channel. It does not prove that the app is genuine, untampered, or running in a trusted environment.
Certificate pinning improves protection by allowing the app to reject unexpected certificates during the TLS handshake. This helps against many interception attempts, although pinning can be bypassed if attackers modify the app or use available tooling. To make pinning more resilient, teams should pair it with runtime application self-protection capabilities (RASP), including anti-hooking and anti-tampering, so attackers have a harder time modifying the app or bypassing the control.
Mutual TLS allows the backend to validate that the client possesses a known certificate. This can help reduce exposure to headless scripts, but it still depends on protecting a private key that may be embedded in the app. If that key is extracted, the trust model weakens.
App attestation is a form of API security that helps prevent backend abuse, including bot and script attacks. It adds another layer by enabling the server to verify that a request came from a genuine app running on a trusted device. When implemented properly, attestation can help detect tampering, suspicious devices, emulators, automated environments, and invalid clients before they can access protected APIs.
| Defense | MITM | MATE | Device bot farms | Headless bot farms |
|---|---|---|---|---|
| TLS | Limited | No | No | No |
| Certificate pinning | Stronger | No | No | No |
| mTLS | Stronger | No | No | Some protection |
| App attestation | Strong, when request-bound | Strong | Strong | Strong |
Choosing the Right Level of Protection
The right strategy depends on the application’s risk profile.
For low-risk applications, standard TLS and basic monitoring may be enough. For business-critical mobile apps handling personal data, financial transactions, proprietary content, or sensitive business workflows, certificate pinning should be paired with runtime protections that make tampering and hooking harder.
For high-risk applications, especially those exposed to fraud, automation, scraping, account abuse, or API misuse, app attestation is essential. In these environments, the backend needs more than a properly formatted request. It needs evidence that the request originated from a legitimate app in a trusted state.
Server-side defenses still matter. Rate limiting, quotas, IP reputation, geo-fencing, behavioral analysis, and web application firewalls can help reduce abuse. But they work best when combined with mobile-specific protections that give the backend more context about the client.
Cloud teams already think deeply about identity, trust, and access across infrastructure. The same mindset now needs to extend to mobile apps. Securing the API is no longer enough. The backend also needs to know whether it can trust the app on the other end of the connection.
##
ABOUT THE AUTHOR
Michael Olechna is a Mobile App Security Evangelist and Product Marketing Manager at Guardsquare, where he focuses on the next era of mobile app development. His role underscores the importance of securing mobile applications, especially as cybercriminals increasingly target small businesses. Olechna is also an expert in mobile app security. His work aims to ensure that software remains both fast and reliable by holding AI-assisted code to the same rigorous standards as manual code.