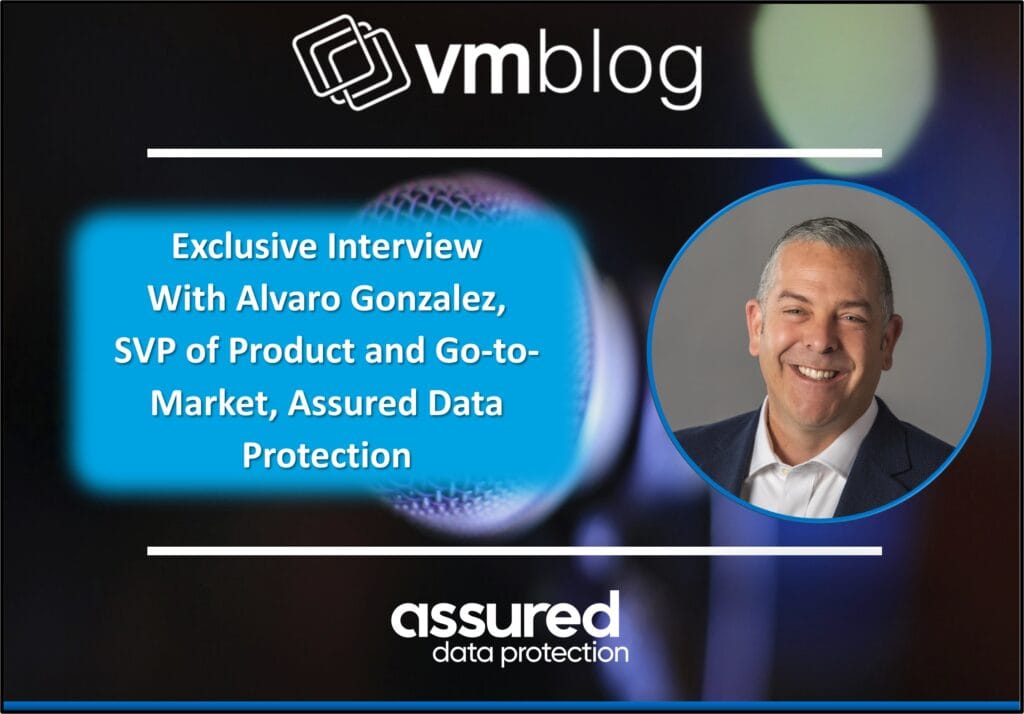
Ransomware has done more than disrupt IT operations, it has moved disaster recovery conversations straight into the boardroom, and with that shift comes a new set of expectations for what “resilience” actually means. Many organizations still treat cyber recovery like a routine backup-and-restore exercise, but as Alvaro Gonzalez, newly named SVP of Product and Go-to-Market at Assured Data Protection, explains, that mindset leaves companies dangerously unprepared for threats that don’t play by predictable rules. In this VMblog Q&A, Gonzalez unpacks why recovering from a cyber event is a fundamentally different challenge than recovering from an ordinary outage, and why the specialized expertise required often lives outside what internal teams can realistically maintain on their own.
Gonzalez’s own role, combining product strategy, technology alliances, and marketing under one seat, mirrors the broader argument he makes throughout this interview: that fragmented approaches, whether inside an organization’s leadership structure or across its resilience strategy, create the exact gaps that adversaries exploit. Drawing on a career spanning cloud, colocation, telecom, and managed services, he offers a candid look at how AI-driven threats are accelerating the race between attackers and defenders, what buyers should actually demand from a managed resilience provider, and why treating recovery as a network-wide “kill chain” problem rather than an isolated IT task will define which organizations withstand the next incident.
Assured Data Protection was also just recently named Rubrik’s Global MSP Partner of the Year 2026.
++
VMblog: What exactly is your new role and why does this role exist now?
Alvaro Gonzalez: My new role as Senior Vice President of Product and Go-to-Market brings together three functions that had been operating in separate lanes at Assured: product strategy, technology alliances, and corporate marketing.
The position was created as Assured reached a stage where running them independently was no longer the most effective way to operate. Bringing these three functions together facilitates tighter coordination that directly impacts how quickly and effectively we can execute.
As we continue scaling globally, greater alignment creates greater speed. Product decisions need to inform partner strategies, partner feedback needs to shape product development, and both need to be reflected consistently in our go-to-market execution. Tighter coordination creates a more direct line between what we build, who we build it with, and how we take it to market.
VMblog: Where do the traditional silos between product, alliances, and marketing cause the most damage?
Gonzalez: I wouldn’t say the silos caused damage outright, but running product, alliances, and marketing as separate functions creates friction and slows execution as we scale.
Each function tells its own story: product has a story about what we built and why, marketing has a story about how it matters to the market, and alliance sellers have a story about how we fit into a partner relationship they already own. When those aren’t connected, product roadmap decisions don’t make it into alliance conversations quickly enough, and alliance relationships don’t shape the roadmap the way they should.
Partners and customers are usually the first to feel that gap, whether it’s inconsistent messaging, slower execution, or missed opportunities to bring the right solutions to market. Bringing these functions together is how we make sure partners and customers get one coherent experience with Assured, not three different ones.
VMblog: The industry talks constantly about cyber resilience, but many organizations still approach this issue as a backup and recovery problem. Why is that and is it changing?
Gonzalez: Changing a frame that’s worked for a long time is hard, and that’s really what’s happening here.
Backup and recovery used to be a drag race: go fast, go straight, and the job’s done. Cyber resilience is a Le Mans race: a technical track with curves that punishes anyone who hasn’t prepared for what’s around the next corner.
What’s forcing the shift is that ransomware and cyber incidents have pushed disaster recovery out of the IT department and onto the board agenda. That changes who’s asking the questions and what answers they expect.
Treating cyber resilience as a backup and recovery problem leaves you without the specialized expertise a real cyber recovery requires, as opposed to a routine operational recovery. That’s one reason we’re seeing organizations turn to managed cyber resilience providers. Recovering from a cyber event now requires specialized expertise, operational discipline, and repeatable processes that many internal teams simply don’t have the resources to maintain on their own.
The businesses that learn this the hard way often become the examples everyone else studies when deciding whether to modernize their own resilience strategy.
VMblog: The managed services market is crowded, and vendors are pitching resilience hard right now. How does a buyer cut through all the noise and evaluate whether a provider can actually deliver?
Gonzalez: Start with focus. There can be an argument There is a real argument for broad, generalized service catalogs when the stakes for a given service are relatively low. But when the stakes are high, specialization matters.
Recovering from a cyber event isn’t the same thing as recovering from a routine outage.
Buyers should look for providers that have built their business around resilience outcomes, not providers that have simply added resilience to a much broader services portfolio. Anyone retrofitting resilience onto a generalized practice tends to show it, usually right when it matters most.
VMblog: Everyone claims to be outcome focused. What specific outcomes should organizations demand from a cyber resilience provider, and how should they measure success?
Gonzalez: I look at three layers. The leading indicator is still recovery time objective (RTO) and recovery point objective (RPO), but with one addition: how fast can the provider find and validate a clean restore point, one that doesn’t reintroduce the same problem or a chain of new ones? The providers worth paying attention to can walk you through that process in real detail and show you how their toolset actually performs against it.
The ongoing indicator comes from testing those restorations regularly and watching whether the provider and the platforms they use keep evolving against new threats.
The trailing indicator is net retention: are customers staying, and are they adding services as new ones become available?
Taken together, a leading, an ongoing, and a trailing indicator give you the real picture.
At Assured, cyber resilience has been our focus for ten years now, and a specialist doesn’t stay a specialist for a decade without delivering. Assured also occupies a unique position as Rubrik’s largest global MSP and winner of this year’s Global MSP of the Year award, combining deep partnership with one of the industry’s leading cyber resilience platforms and a decade of operational experience delivering managed recovery outcomes at scale. There’s nowhere to hide on either front.
VMblog: You’ve worked across cloud, colocation, telecom, and managed services. What does that cross-sector view tell you about where enterprise resilience is headed that someone who’s only lived inside the backup and recovery world might not see?
Gonzalez: Threats behave like water. They’re always finding a new way in, and if you block one path they find another.
Working across cloud, colocation, telecom, and managed services has shown me that even great technology fails without great execution behind it, and great execution without great tools also falls short. You need both.
At global scale, that gets more complicated. A product definition that works in one region doesn’t always translate cleanly to another market, and an alliance relationship with a strategic partner like Rubrik only delivers value downstream if it’s managed consistently across every geography you operate in.
The risks organizations face aren’t isolated anymore. They’re networks of networks. Disrupting one system often creates consequences somewhere else that aren’t immediately obvious. That’s why it’s called a kill chain. You have to think about the whole chain, not just the link in front of you.
VMblog: Over the next two to three years, what changes do you think will have the biggest impact on cyber resilience providers? (AI-driven threats, regulatory pressure, cloud complexity, or something else entirely?)
Gonzalez: AI-driven threats will be the biggest driver of risk, and that shouldn’t surprise anyone.
Technology has always been a race between new threats and new defenses, but what AI changes is the speed of that race.
The real story is the widening gap between how fast vulnerabilities are found and exploited, and how slowly organizations patch or retire the systems exposed by them. Patching doesn’t generate revenue. It’s a cost center for the vendors who write the software and a cost center for the businesses that run it, and it takes time that competes with everything else on an IT team’s plate. That gap is getting harder to close right as the value of what is being protected keeps going up.
Regulatory pressure and cloud complexity will continue to influence resilience strategies, but they’re all interacting with the same underlying challenge that is organizations are struggling to keep pace with the speed at which threats evolve.
##
Alvaro Gonzalez, Senior Vice President of Product and Go-to-Market, Assured Data Protection
Alvaro Gonzalez is Senior Vice President of Product and Go-to-Market at Assured Data Protection, a newly created global leadership role brings together product strategy, alliances, and corporate marketing under a unified structure, to improve coordination across Assured’s go-to-market operations and support the company’s continued international growth. He leads all three of these key operational pillars. His role reflects Assured’s focus on creating a more integrated approach to product development, messaging, partner engagement, and market expansion as demand grows for managed cyber resilience and operational recovery services.