
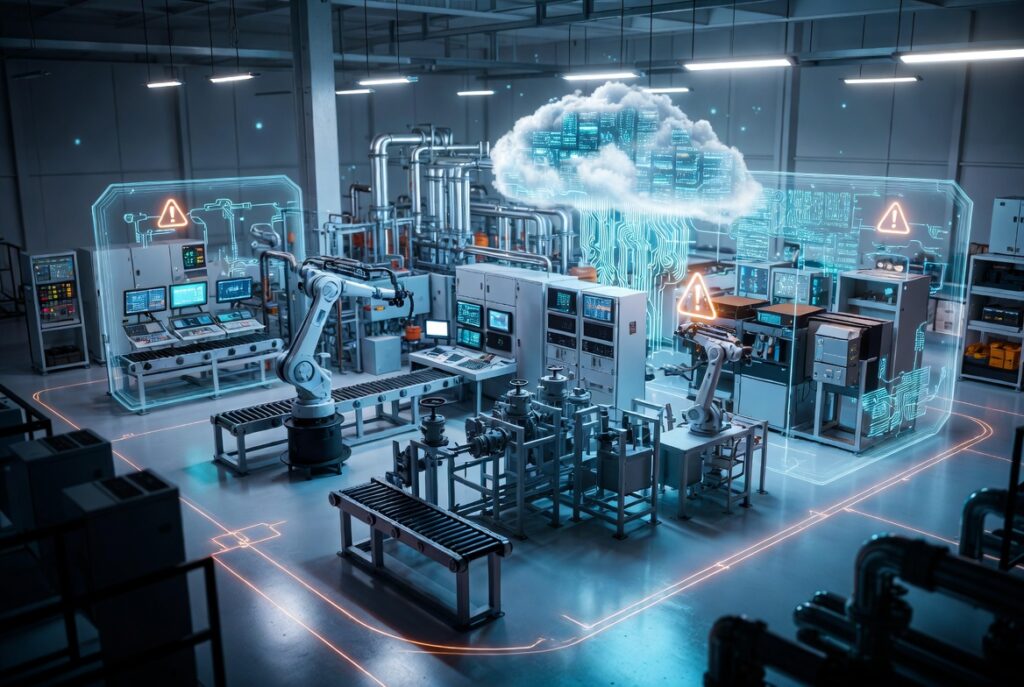
Industrial control systems (ICS) were built to run production, not to defend themselves. As they now connect to the rest of the enterprise, that gap is becoming the industry’s critical security problem.
Production networks were not designed with connectivity in mind. They were once completely cut off from enterprise IT networks, but today they communicate with cloud-based applications, perform remote maintenance, receive updates via pipelines, and use identities across different environments.
Cloud connectivity and remote access have driven many improvements, but they have also changed how these environments think about security. Critical services organizations must understand how risk moves throughout their whole attack surface, from enterprise IT to operational technology (OT), and determine the risks that can affect production and safety.
That movement of risk explains why exposure management is becoming an integral part of modern OT security strategies.
Why does OT stay invisible to security programs?
Most organizations have a reasonable understanding of their enterprise IT assets. However, operational plants often use equipment that has been in service for years because it still performs reliably.
Industrial control systems (ICS) were not designed to work in harmony with modern security tools, and there is rarely a way to shut them down for scanning. An interruption, even if temporary, can cause production delays or create safety risks. Running production safely and on time almost always takes priority.
Responsibility is usually shared as well. The engineering team knows what assets the factory has and how its equipment is used to run daily activities. The security team understands emerging threats, business risks, and enterprise networks.
However, no one has the full picture of how all the assets fit together in the broader context.
Nobody has visibility over everything. Maintenance projects add new devices. Remote contractors connect to networks for diagnostics or support. Old legacy systems remain in service long after the documentation has fallen out of date.
Over time, those small changes create blind spots that are easy to miss. Before an organization can start to mitigate risk, it must be confident that it knows what is connected.
How has IT/OT convergence expanded the attack surface?
The old distinction between enterprise IT and operational technology is becoming harder to maintain.
Software updates increasingly move through continuous integration and continuous delivery (CI/CD) pipelines. Vendors troubleshoot equipment remotely instead of visiting sites in person. Operational data flows into cloud platforms that support analytics, predictive maintenance, and business reporting. What were once isolated operational environments now exchange information with enterprise systems every day.
Each change makes operational environments more capable and efficient. Each one also creates another connection that security teams need to understand and protect. A single trusted connection may support legitimate business operations, but it can also become part of a larger attack path if it is compromised.
For those in DevOps and platform engineering roles, this is a familiar concept. Not only are these technologies changing how teams develop and deliver software, they are now also reaching into industrial environments. Remote access capabilities, identity management solutions, software chains, and cloud-based infrastructures are now all possible points of entry for attackers into production environments.
As you automate more processes and connect more systems, the line between enterprise IT and OT continues to blur.
What does exposure management add for OT?
Traditional vulnerability management answers one question well: where are your vulnerabilities?
Exposure management answers a different question: which of those vulnerabilities actually increases your business’s risk?
In operational environments, where hundreds of findings may compete for attention while maintenance windows are still limited, this is important. Verizon’s 2026 Data Breach Investigations Report revealed that stolen credentials and unpatched vulnerabilities were cited as the two leading causes of manufacturing breaches in 2025, with each responsible for 41% of incidents in the sector.
A modern exposure management program combines asset information from IT, cloud, identity, and OT environments, then adds context around exploitability and business impact. Exposure management also helps security teams understand how individual weaknesses combine into exploitable attack paths between enterprise and operational environments.
That broader perspective supports more practical remediation decisions. A vulnerability on an isolated engineering workstation rarely deserves the same urgency as one that creates a route toward production-critical assets.
How can organizations start without disrupting operations?
Industrial organizations rarely have the luxury of starting from scratch. New security programs have to fit around equipment that is already running and production schedules that cannot simply stop for assessment.
For this reason, most companies opt for passive monitoring to start with: they can discover assets, understand communication patterns, and develop a full list of assets without generating any traffic that might affect critical equipment.
Afterward, the process becomes organizational and not technical. There needs to be coordination between engineering and security so they share a common perspective on the environment without maintaining separate lists of assets and priorities.
Slow deployment proves advantageous, too. One single production location alone will uncover problems in documentation, ownership, and operations that are much simpler to fix prior to full-scale deployment.
Industrial organizations have lived with incomplete inventories and disconnected spreadsheets for years; however, as operational environments become more connected, maintaining that approach becomes increasingly difficult. Visibility across IT, OT, cloud, and identity provides security teams with a stronger foundation for deciding where to focus first.
##
ABOUT THE AUTHOR
Joe Pettit is the owner of Information Security Buzz, and an award-winning Managing Editor during his time running Tripwire’s State of Security blog. Joe specializes in breaking down complex security topics, making it easy for readers to consume. His favorite topics to cover include vulnerability management, compliance regulations, and industrial cybersecurity.





