Industry executives and experts share their predictions for 2025. Read them in this 17th annual VMblog.com series exclusive.
By Eyal Benishti, CEO, IRONSCALES
Like most industries, the cybersecurity landscape has been forever changed by the emergence of modern AI. While organizations are already beginning to feel the effects of AI-enabled cyberattacks, they unfortunately have a whole lot more in store for them over the year ahead.
Based on our own platform data, mounting industry concern, and other leading indicators, it’s become clear that threat actors will be leveraging AI to enhance their hacking efforts in a variety of ways in 2025-using the technology to both develop novel strategies and supercharge existing ones.
Here are three ways threat actors will use generative AI that security teams will need to be prepared for in 2025:
1. To Create Increasingly Creative Social Engineering Strategies
From deepfakes to LLMs, AI has equipped threat actors with a toolset of unprecedented power and utility. While 2024 saw many of these tools hit the stage, 2025 will be the year in which they begin to come of age. For example, we’re already beginning to see a growing number of voicemail phishing (a.k.a. vishing) attacks, as well as attacks in which attackers are using malicious links embedded in email attachments – both of which are proving to be some of the most effective phishing strategies in use today. However, by adding generative AI to the mix, both of these strategies are taking on a whole new level of sophistication. Already, audio deepfake tools enable users to recreate an individual’s speaking voice with less than 30 seconds of source audio. With these pitch-perfect vocal impersonations, already effective vishing attacks will become truly devastating. At the same time, LLMs like ChatGPT have proven to be game-changing social engineering tools when it comes to crafting more effective phishing emails. With LLMs, threat actors are able to write better, more convincing phishing emails (in any number of languages) with minimal time and effort. As a result, we will almost certainly see strategies involving malicious email attachments become even more prevalent and effective in the year ahead.
2. To Develop Synthetic Online Personalities for Influence and Financial Gain
Not long ago, for most people, the term “deepfake” conjured up images of the pope in a puffer jacket, or viral videos of the Star Wars cinematic universe reimagined as a Wes Anderson production. In the wake of 2024’s historic election cycle, though, the technology has become synonymous with misinformation, disinformation and political influence campaigns. Going into 2025, however, we will see deepfakes take on yet another role in the digital landscape – the creation and commodification of synthetic influencers and audiences. While this phenomenon already exists in a much smaller, and more primitive form – largely through the use of bots, shell accounts, and click farms – I’m confident that 2025 will usher in a new era of fabricated engagement online. With the emergence of generative AI, deepfakes, and other forms of synthetic media, bad actors will be able to create fully-fledged and remarkably convincing internet personalities capable of cultivating sizable audiences by doing things like writing articles, reviewing products, blogging, and even creating podcasts and video series. I also expect there will be a widespread effort to automate these personalities and their content in order to establish substantial online circles that can then be offered up for sale. Alternatively, their services could be used to promote, sell, or undermine whatever product, brand, or ideology the highest bidder may choose.
3. To Code More Convincing, Authentic-Looking Spoofed Web Pages
Malicious actors have been creating “spoofed” web pages for decades. For those not familiar with the terminology, “spoofed” pages are fraudulent recreations of legitimate web pages designed with the intention of deceiving users into mistaking the “spoofed” site for the real thing. Most often, threat actors spoof login pages in order to harvest users’ credentials, which can then be used for unauthorized account access on the legitimate version of the site. While spoofed web pages are far from new, until recently, the inherent limitations of time, energy, and coding skill had placed natural limits on their scale and sophistication. Now, however, generative AI can be used to spoof login pages for well-known brands like, Microsoft 365, Google Workspace, or even industry-specific services for space such as real estate, legal services, healthcare, and higher education. As a result, of these infinitely more diverse, convincing, and easier-to-produce spoofed web pages, we will undoubtedly see higher click-through rates, and the successful collection of individuals’ credentials, which can immediately be turned around and used in devastating account takeovers.
As all of the above takes place, cybersecurity vendors and researchers will undoubtedly be working overtime to develop new, more sophisticated and reliable tools to defend against such attacks. However, at the moment, the threat actors of the world remain a couple steps ahead. In 2025, we can only hope that the hard work and innovation among cybersecurity developers will help us to close that gap before the worst of the damage has been done.
##
ABOUT THE AUTHOR
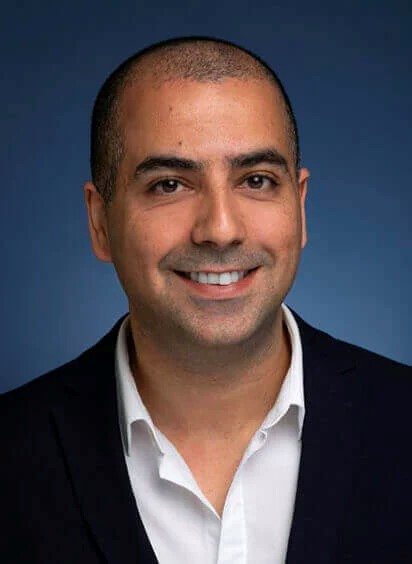
Eyal Benishti is the CEO and Founder of IRONSCALES, pioneering the world’s first self-learning email security solution to combat advanced phishing, BEC, and account takeover attacks.
With over 15 years in the software industry, Eyal has held roles as a security researcher and malware analyst at Radware and a technical lead for information security solutions at Imperva. He also held R&D positions at Comverse and Amdocs.
Eyal earned his bachelor’s degree in computer science and mathematics from Bar-llan University in Israel and has been passionate about cybersecurity from a young age.