Industry executives and experts share their predictions for 2025. Read them in this 17th annual VMblog.com series exclusive.
By Jon Check, Vice
President, Cyber Protection Solutions, Nightwing
With the current cyberattack landscape, we must
always look ahead to ensure we are preparing for the next threat, implementing
the most advanced technology, and adopting the latest regulation or policy.
With the new year approaching, it is the perfect time to ensure we are doing
just this.
I connected with those across the Nightwing
organization, and they have high expectations for 2025. Check out their
insights below as they analyze the growth of AI in more ways than one, cyber
regulation, and advanced analytics.
John DeSimone, Chief Executive Officer
AI will continue to reshape offensive cyber
operations in 2025 by enhancing data visibility and streamlining threat
intelligence – vital for both defense and attack strategies. It facilitates
quicker decision-making and improves the prediction and response to threats.
However, this technology also benefits adversaries, enabling them to conduct
more sophisticated attacks, such as creating deepfakes, developing advanced
malware, and disseminating misinformation widely on social media. To remain one
step ahead, organizations will need to take a careful look at how they are
utilizing AI technology by first understanding their exact mission. If leaders
do not understand what success looks like, they will not be able to apply their
AI solutions properly to effectively combat AI threats.
With that said, the ethics surrounding the use of AI
technology will grow exponentially as the new year progresses. This is due to
the rapid integration of AI into security frameworks, bringing significant
risks, particularly in national security contexts. The reliance on AI for
critical decision-making demands a high level of transparency and
accountability. The increasing amount of international guidelines for secure AI
systems development underscores this urgency. There is a critical need for
ethical AI practices in security measures, particularly in the aspects of
transparency, traceability, and auditability. Organizations must make it a
priority to implement these ethical practices to understand and mitigate biases
in AI decision-making, ensuring that AI actions align with ethical and legal
standards.
++
Dylan Owen, Chief
Information Security Officer
Heading
into 2025, there are several areas where cyber regulation and compliance could
have an impact on organizations. The first instance is with the Cybersecurity
Maturity Model Certification (CMMC). For any companies doing business with the
Department of Defense, this regulation was approved at the end of 2024 and will
start the implementation phase in 2025. While the rollout will be accomplished
over several years, companies will need to start, if they already haven’t,
preparing their infrastructure to meet the requirements, which could take a
while and incur some costs to upgrade systems.
Other
areas that could be impacted by regulation are:
- AI and Machine Learning (ML): With the boom in AI capabilities and many
industries looking to take advantage of this potentially transformative
technology this will more than likely trigger regulation on the use, especially
in already highly regulated industries like Finance and Healthcare. There will also be some guidelines around the
ethical use of AI to address things like bias, transparency and accountability.
- Data Privacy and Protection:
Privacy laws are still a patchwork around the country and world. I would expect
a push to develop a standard privacy law for the United States.
- Cybersecurity Incident Reporting
and Disclosure: There are several Incident and
reporting regulations that have been discussed but not yet finalized which
could happen in 2025. CISA has been working on a reporting rule for Critical
Infrastructure that could be finalized in 2024. TSA has also proposed rules for
surface transportation companies as well as pipeline owners/operators that
could have a significant impact on organizations. It’s unclear what if any
impact the presidential election results would have on these regulations. In
general, Republican administrations have been against further regulations of
industry but in the last Trump administration significant progress was made in
the cybersecurity space as CMMC was first introduced during that
administration. Cybersecurity is typically a non-partisan topic with both
parties interested in making progress.
++
Chris Jones, Chief Technology Officer and
Chief Data Officer
The acceleration of AI has brought
an opportunity for advanced analytics, enabling organizations to exploit the
data that is available to them. This is especially significant given the
growing global data landscape, adding complexity, and requiring organizations
to evolve their approach to data fusion and analysis so they are equipped to
meet their strategic goals. Utilizing available and accessible data can also
point organizations to new insights, drive more efficient operations, create
new market opportunities, and meet employee training needs. Yet, the potential
of any strategy is predicated on having a sound data environment.
In 2025, Chief Data Officers
(CDOs) must also bring new value to their roles by ensuring their organizations
are capitalizing on their accessible data. While the CDO position has largely
been about compliance and risk management, it must now evolve to accomplish its
traditional data management responsibilities while also demonstrating to
leadership the opportunities data analytics can hold if the right strategies
are put in place. There’s a significant contrast between a CDO’s defensive
approach to compliance and their capacity to enhance business and mission
results. A CDO must work to close this gap in the new year.
++
Organizations
should embrace these insights to position themselves for success in 2025. While
the future holds uncertainties, implementing the strategies outlined by these
leaders will enable them to better harness AI, navigate evolving regulations,
and maximize the value of their data with greater confidence and agility.
##
ABOUT THE
AUTHOR
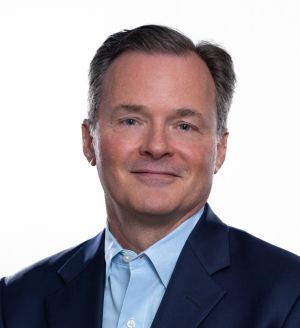
Jon Check is
Vice President of Cyber Protection Solutions for Nightwing. He leads the team
that delivers proactive cybersecurity solutions protecting organizations from
the ever-evolving cybersecurity threat and delivering next-generation
technology and enterprise solutions for customers across Nightwing’s cyber
portfolio.
Check led the
CPS team at Raytheon before his time at Nightwing. He joined Raytheon from CSRA
Inc., where he was Vice President of the digital solutions organization. He was
responsible for direction, strategy and operations of the services provided
from CSRA’s delivery centers.
Prior to CSRA,
Check was Vice President of the solutions organization at Computer Sciences
Corporation’s North American public sector and before that was executive
operations manager of global business services for IBM within IBM’s public
sector.
In July 2019,
he received a non-legislative citizen appointment from Virginia Speaker M.
Kirkland Cox to the Secure and Resilient Commonwealth Panel, an advisory board
in the Executive Branch of Virginia’s government. The panel was established in
2004 and its primary focus is on emergency management and homeland security
within the Commonwealth to ensure that both state and local governments are
prepared to address risks from man-made and natural disasters.
Check serves
as chairman for the National Cyber Security Alliance, chairman of the Executive
Mosaic 4?24 Cyber group, Red Hat strategic advisory board member, and AFCEA DC
board member. He holds a Bachelor of Arts in environmental science from the
University of Virginia.