

Industry executives and experts share their predictions for 2026. Read them in this 18th annual VMblog.com series exclusive.
By Paul Laudanski, Director of Security Research at Onapsis
In 2026, I expect to see escalating cyber threats against our most business-critical applications, unless governments step up with stronger legislation and organizations finally embed Security by Design into every layer of their operations.
In 2025, we witnessed a rise in critical attacks stemming from the unprecedented SAP NetWeaver zero-day, CVE-2025-31324 – an incident neither SAP nor I had ever seen before. The incident taught us three key lessons for 2026:
- Business-critical apps are a high-value target because attackers know these applications directly impact the revenue, operations and reputation of companies
- Patching is just the beginning – ongoing monitoring, configuration management and threat detection are required to stay secure
- ERP security requires a business and security partnership because ERP systems often fall outside of traditional security teams
It wasn’t an isolated event, with a wave of exploits continuing to follow the incident, but rather the issue symbolizes how the gap between attack and defense has widened.
Artificial intelligence continues to contribute to that gap. We’re seeing technologies like OpenAI’s Sora and other models blurring the line between authentic and synthetic information. Even my team of cybersecurity professionals struggles to trust what we see and hear. Deepfakes are being used to manipulate executives, impersonate candidates in job interviews and exploit unsuspecting employees through super personalized social engineering. In today’s world, the truth is unknown – trust and validity are the real attack surface the industry needs to protect.
Ransomware also remains one of the more profitable tools for a threat actor. We’re inching closer to the age of quantum computing, meaning the foundations of our current encryption methods are going to be tested further. This threat won’t materialize in 2026, but the groundwork is being laid.
A major challenge lies in how we’re architecting security itself. Organizations are not treating security as a business priority, despite the mounting evidence that it’s now more urgent than before. Organizations continue to treat security as a box to be ticked rather than a business imperative.
The demand for the digitization of business initiatives is becoming more intense, and with that, executives feel the pressure to accelerate the process, leaving behind vulnerabilities and bad code. SAP says barely half of transformations go according to plan, and 58% run over budget. In countless transformation projects, I’ve seen firsthand how security is being introduced far too late in the process. By the time security enters the conversation, budgets are spent, and there’s a resistance to change.
This mindset has to change in 2026. Cybersecurity is a business survival issue and must be treated as such. There is an urgent need for legislative accountability. Too often, we’re seeing organizations face no real consequences for neglecting cybersecurity until a crisis occurs. Decision makers must be held personally responsible when negligence leads to catastrophe. If you don’t lock the door and someone walks in, you’re not just a victim. Enforceable policies are necessary for organizations to prioritize security from the start.
We don’t need reactive measures – we need a cultural shift toward Security by Design. That means embedding security in every business decision and every stage of the journey – architecture, development, operations, governance and more. The time to act is now. Heading into 2026, I urge your organization to prepare now by committing to a new standard: No digital transformation without integrated cybersecurity.
##
ABOUT THE AUTHOR
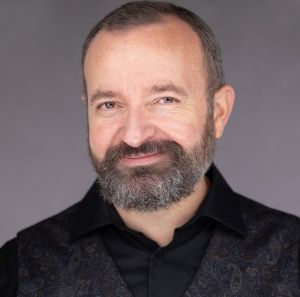
Paul Laudanski, Director of Security Research at Onapsis, brings to his role over twenty years of experience in cybersecurity, threat research and engineering, threat intelligence, and counterintelligence. Paul is also a member of the Onapsis Research Labs team and is dedicated to hunting down vulnerabilities within business critical applications which have helped to remediate over 1,000 zero day vulnerabilities within SAP and Oracle applications. Paul holds a BA in mathematics from Rider University and lives in Tacoma, Washington with his family.






