By Adam Sandman
You know you need to address your security and compliance issues-especially in an era where data breaches and regulatory requirements have become significant concerns. Global cyber-attacks increased by 7% in Q1 2023, with each firm facing an average of 1,248 attacks per week, according to Check Point’s most recent report, and 1 in 31 organizations worldwide experienced a weekly ransomware attack during the first quarter of 2023.
But where should you start? There are so many options today; it can be daunting. Should you go the Software as a Service (SaaS) route? Look for an on-premises solution? Or turn to a private cloud infrastructure?
Here are my top five tips for navigating this complex landscape and finding the best technology and/or solution suited to your organization.
1. Large Companies May Find SaaS Solutions are Less Cost Effective
Adopting SaaS products has allowed companies to deploy and use new technologies more rapidly. It also allows companies to focus on their core business instead of managing systems, servers and IT assets in-house. However, large companies are now finding that SaaS options can result in higher operating costs than a traditional IT organization, depending on the pricing models for large enterprises.
2. Consider a Self-Hosted or Private Cloud Solution Where Sensitive Data is Concerned
When looking to ensure high security against cybercrime and other hacking-related events, companies often need to balance the advantages of SaaS (security taken care of by experts) with the benefits of a self-hosted or private cloud alternative (limiting access to the data, choice of data residency and more control). In other words, an on-premises or private cloud solution often offers a higher level of protection against cybercrime where sensitive data is concerned.
3. Find Out Whether Your Industry or Geography Dictates What Solution You Must Use
Companies that work in specific industries or geographies may have the choice dictated to them (data residency rules, GDPR, HIPAA, or classified intelligence data). Find out whether your industry or location requires a particular approach or solution before going down any rabbit holes. Heavily regulated industries such as healthcare, banking, aviation, and defense often require unparalleled data sovereignty and the most secure hosting capabilities imaginable.
4. Investigate The Security Features and Liability Protection of SaaS Solutions
When evaluating SaaS companies and contracts, companies should understand key security features, including certifications (SOC2, ISO 27001), data residency, company ownership, geographical location (NATO vs. non-aligned), and liability protection. For example, a SaaS service may claim to relieve the burden for its customers, but if its contract assigns all liability to the customer, is that truly the case?
5. Evaluate the Customer Service Capabilities and Commitment of Each Solution
Do you have in-house capabilities or an IT team that simply needs an extra tool? Or a one-stop, turnkey solution to manage every step of the application lifecycle, with seamless integrations, easily accessible audit trails, and built-in instant messaging capabilities for easy, in-application communication? In other words, if you need a soup-to-nuts solution, you might want to consider options with more robust customer service offerings than if you simply need a stopgap for your already sizable team to implement.
At a time when 340 million people have felt the impacts of publicly-reported data breaches or leaks in 2023 alone, according to a public data breach tracker created by the U.K. news site The Independent, this has never been a more mission-critical issue for companies in every industry to solve. With cyber vulnerabilities skyrocketing 589% and the number of assets organizations are managing increasing by 133% year-over-year from 165,000 in 2022 to 393,419 in 2023, according to a new State of Cyber Assets Report (SCAR) report, this is the time to address the multiplying security vulnerabilities.
##
ABOUT THE AUTHOR
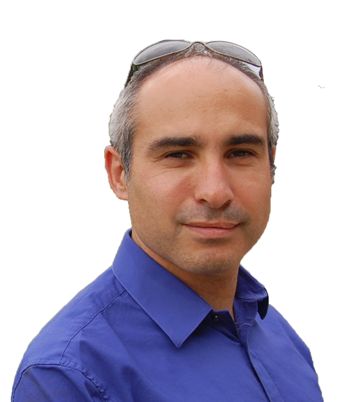
Adam Sandman, who founded Inflectra in 2006, has been a programmer since the age of 10. Today, Adam serves as the company’s CEO. He is responsible for product strategy, technology innovation, and business development. He lives in Washington, D.C., with his family.
Prior to founding Inflectra, Sandman worked as a director for Sapient Government Services, where he was in charge of development with the U.S. Marine Corps. and other government agencies, and was responsible for leading many capture teams and writing whitepapers and position statements to build Sapient’s reputation as a leader in the defense space. He studied physics at Oxford University.