Industry executives and experts share their predictions for 2026. Read them in this 18th annual VMblog.com series exclusive.
By Shahar Man, Co-Founder and CEO, Backslash Security
The year 2025 saw AI coding assistants move from novelty to mainstream, accelerating software development in unprecedented ways. In particular, vibe coding-a fast, intuitive style of coding where developers rely on AI to generate and modify code using common language prompts-is revolutionizing code generation. On one hand, vibe coding empowers developers to produce code at record speed; on the other, it introduces unique security challenges. As we look to 2026, the rise of autonomous coding agents and AI-driven development workflows will reshape how we think about the security of developer environment, code, applications, and the software supply chain. Here are my predictions on how vibe coding will impact cybersecurity and why it will demand a fundamental shift in software security.
The battlefield moves into the developer environments
Developer workstations and integrated development environments (IDEs) have never received special attention from security teams. AppSec teams have been focusing on code vulnerabilities and artifacts, not on infrastructure, and developer workstations have been treated just like any other endpoint – ignoring the special access and impact on a company’s applications and code IP they have.
AI-native coding is going to change all of that. Essentially introducing many potential backdoors into the developer environment, AI coding agents and MCP (Model Context Protocol) servers are suddenly allowing attackers to insert themselves deep into the code factory, creating supply chain risks, poisoning opportunities, and taking advantage of historically weak security controls.
Much of this today falls in the cracks between IT, application and product security areas of responsibility, but the nexus of threats that the vibe coding ecosystem creates should not be ignored any further.
A Major MCP Breach Will Be a Wake-Up Call
Nothing calls for change in cybersecurity quite like a high-profile breach. Given the above mentioned risks, in 2026 we’ll see the first large-scale cyber incident traced back to an autonomous coding agent running with too much trust and too little oversight.
Consider this nightmare scenario: a malicious backdoor quietly injected into enterprise software by a rogue AI coding tool or an exploited component of the AI coding supply chain. Because vibe coding allows for code to propagate from development to production faster than ever, this means a poisoned output from an AI could spread to critical systems before human code reviewers even notice.
I expect that a significant breach involving a Model Context Protocol (MCP) server or AI coding agent will finally make headlines in the coming year. When this happens, it will become painfully clear that innovation in AI coding has outpaced the guardrails meant to secure it. Organizations have been blindly integrating output from AI coding assistants, and a breach would expose how deeply enterprises have trusted these AI code without proper scrutiny. The fallout will trigger a sober re-evaluation of AI coding agents in the software development lifecycle.
Traditional AppSec Tools Fall Short in the AI Era
Security and IT teams are already well-aware that traditional application security tools like SAST and SCA are inadequate in securing AI-generated code. That’s because in an era of AI-generated code, static scanners simply can’t keep pace with the evolving, dynamic behavior of autonomous coding agents.
While traditional AppSec tools excel at catching known vulnerable patterns in code created by humans, they struggle to understand how or why a piece of code was produced. This becomes especially problematic when vibe coding introduces novel code constructs or rapidly refactored segments that don’t match any known vulnerability signature, causing them to slip through traditional scans unnoticed. Moreover, static tools provide a snapshot in time whereas AI code generation can happen continuously and fluidly.
As vibe coding reshapes how software is written and modified, security must move beyond just analyzing what the code does and start considering how it was created. 2026 will prove that a purely static, point-in-time defense is no match for a non-deterministic, AI-fueled development pipeline. The industry will begin shifting toward more contextual and continuous approaches that can follow AI as it writes and alters code in real time.
Vibe Coding Will Resurface Old, Obsolete Vulnerabilities
The non-deterministic nature of AI-generated code means that even small AI-driven changes can have unpredictable ripple effects on an application’s security posture. In practice, each AI-suggested “improvement” carries the risk of quietly undoing past security fixes.
For example, an AI coding agent might reintroduce an input validation flaw or path traversal vulnerability that a human developer had previously patched, simply because the AI lacks context of historical bug fixes, or just prefers to ignore them.
In 2026, this pattern of old vulnerabilities returning in new code will expose a critical blind spot in current AppSec practices. Security teams will be forced to rethink how they test and continuously monitor code written by AI. It won’t be enough to trust that once-patched issues stay patched. Every new code iteration, human or machine-made, could potentially open a hole that was once closed.
Securing the SDLC Will Evolve into Real-Time, AI-Aware Defense
Because of the potential risks at hand, we’ll witness a shift towards vibe coding security 2026. Security tools and practices will become AI-aware, continuous, and woven into the fabric of code generation.
This new paradigm will merge traditional control mechanisms with real-time, context-rich insight into both human and AI-generated code. Instead of scanning code only after it’s written, security will shift to securing AI coding as it happens, providing preemptive fixes and guardrails. In this way, the industry will begin securing both human and machine-written code in real-time, closing the gap that vibe coding has opened.
Those who embrace this AI-aware, real-time security approach and enforce strong governance on AI code generators will be ahead of the curve. Those who cling to old tools and complacent trust in machines will risk devastating breaches and regression in their security maturity.
##
ABOUT THE AUTHOR
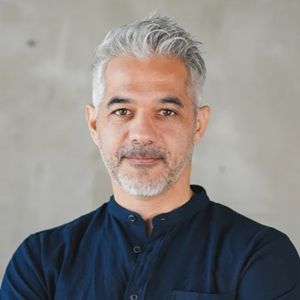
Shahar Man is a seasoned technology leader with deep experience in engineering, AppsSec, DevOps and product management. As the co-founder and CEO of Backslash Security, he is dedicated to evolving application security to meet the needs introduced by AI code development. Previously, Man held leadership roles at Aqua Security and SAP, where he spearheaded strategic cloud and DevOps initiatives.