Industry executives and experts share their predictions for 2026. Read them in this 18th annual VMblog.com series exclusive.
By Lori MacVittie, Distinguished Engineer & Chief Evangelist, F5
Everyone is still obsessing over model bias, hallucination rates, and prompt injection techniques. Fine. But the real security crisis is not hiding in prompt and output layers, it’s hiding in the delivery layer that sits between agents, identity, and inference. The uncomfortable prediction for 2026 is this: inference will outgrow the security foundations that enterprises have trusted for decades. PKI, the quiet backbone of digital trust, will strain under a workload that was never designed for it.
Inference is not a human-driven transaction. It is not a login and a handful of API calls. It is a sustained, recursive interaction pattern created by autonomous agents that run at machine speed and multiply themselves in ways that break every static identity concept we have. When every request is generated by a different instance of an agent, and each instance has a sub-minute lifespan, the certificate-based identity model collapses. It does not matter how mature your CA is. It does not matter how fast your enrollment pipeline has become. Certificates assume stability. Agents assume volatility. This is the textbook definition of a mismatch.
The industry has not admitted this yet, but the data points are everywhere. Enterprises adopting agents expect explosive identity growth, increased impersonation attempts, more privilege boundaries, and an inability to attribute actions to specific agents. These are not theoretical future problems. They are clear warnings that identity has become the weakest part of the inference architecture. PKI thrives in environments where entities endure. Servers live for years. Devices live for months. Even short-lived service identities last long enough for the certificate lifecycle to make sense. An agent that spins up for a few seconds has no practical path through this machinery.
This creates a prediction that security teams will not want to hear: within the next three years, certificate authorities will become bottlenecks for AI-driven applications. Authentication and authorization pipelines based on static credentials cannot scale to millions of autonomous inference calls from short-lived actors. The natural workaround will be to mint broader certs and share identities across agent classes. That shortcut will create lateral movement paths that make today’s API key misuse look quaint.
Inference will force a shift toward ephemeral, attestation-based identity. Agents will not carry long-lived certs. They will carry short-lived, signed proofs that blend policy, context, and behavioral expectations. The identity of an agent will not be who it is, but what it is allowed to do. Think of it as capability projection rather than entity authentication. PKI will still exist but buried deeper in the stack. It becomes the trust anchor for issuing ephemeral credentials rather than the identity mechanism for every actor in the system.
This brings us to the last prediction: delivery infrastructure will become a major gatekeeper of identity. Not IAM. Not the CA. The traffic management layer. Agents operate through APIs. They negotiate policy, resource limits, and routing decisions through the delivery fabric. The only place you can reliably enforce identity, privilege, policy, cost boundaries, and behavioral checks is the layer that touches every request. This is what enterprises are already signaling. They see the highest operational impact in the token, prompt, and routing layers. Those are delivery layers, not IAM layers.
Multiple reports consistently rank over-privileged agents, identity sprawl, and agent-to-agent impersonation as the top realized risks, far ahead of classic prompt injection or hallucination. As of December 2025, multiple confirmed incidents involving autonomous AI agents have already occurred, and none of the significant ones were caused by model hallucination. They were caused by an identity collapse at the inference boundary. An agent used a model to generate malicious code and exfiltrate data. In November, a rogue autonomous agent drained around $531k from a decentralized treasury through privilege escalation and unauthorized transactions. The threat is extant and recognizing what needs to change is the first step.
Inference is not safe or secure by default. It demands a rethinking of identity, trust, and delivery. Those who recognize this early and build agent-aware identity, ephemeral trust models, and behavioral enforcement into the fabric of traffic management will define the next era of application security. The rest will spend years chasing problems their architectures were never built to solve.
##
ABOUT THE AUTHOR
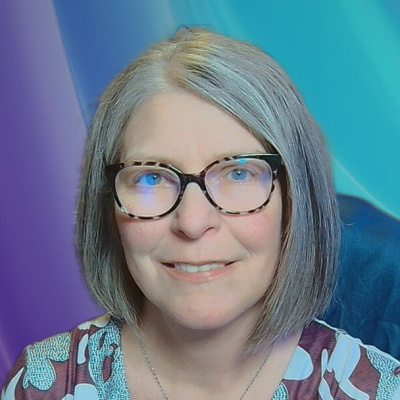
Lori MacVittie is a Distinguished Engineer & Chief Evangelist in F5’s Office of the CTO with an emphasis on emerging architectures and technologies including cloud and edge computing, digital transformation, and application delivery. MacVittie has over twenty-five years of industry experience spanning application development, IT architecture, and network and systems’ operation.
Prior to joining F5, MacVittie was an award-winning technology editor at Network Computing Magazine and an enterprise architect who helped lead a global transportation and logistics firm into the Internet age. MacVittie has developed software for Nokia phones, Autodesk, and regional telecommunications firms. She co-authored the CADD profile for ANSI NCITS 320-1998 and is a prolific author with books spanning security, cloud, and enterprise architecture.
She holds an M.S. in Computer Science and particularly strong opinions about cheese and gaming systems.