Industry executives and experts share their predictions for 2026. Read them in this 18th annual VMblog.com series exclusive.
By Sean Tufts, Field CTO, Claroty
Entering 2026, organizations are navigating an inflection point in critical infrastructure security. According to research, nearly half of security professionals say that shifting economic policies and geopolitical tensions are increasing cyber risk to their cyber-physical systems (CPS), underscoring the modern complexities of safeguarding essential operations. This shift reflects a broader reality: Operational technology (OT) has become deeply interconnected, increasingly targeted, and foundational to both organizational and national resilience. The forces shaping this landscape are accelerating, and three trends in particular will redefine how operators, governments, and security teams prepare for the year ahead.
OT Security Engineers Will Become One of the Fastest Growing Job Titles in Cybersecurity
For years, OT security lacked a formal home inside most organizations with responsibilities often being assigned to local plant network administrators, control systems engineers, or the most technically curious team member onsite. While these individuals have a deeper understanding of industrial processes than most, they are rarely equipped with the full spectrum of cybersecurity expertise needed to handle modern threats.
This antiquated mindset is coming to an end and rightfully so. The rapid growth of CPS security programs across manufacturing, energy, transportation, and pharmaceuticals has created a converged security demand that traditional IT (information technology) or OT teams individually cannot meet. Organizations need experts who can bridge both domains with equal fluency. In 2026, the job market will reflect this. Expect to see the title “OT Security Engineer” appear widely on LinkedIn, Indeed, and specialized security job boards.
The requirements for these roles will be rigorous. A candidate may need a CISSP, a decade of PLC experience, familiarity with industrial networking protocols, hands-on work with incident response frameworks, and the ability to translate complex risks into operational language. It will resemble a unicorn job description, but it reflects a real need. As organizations harden their critical systems and begin digitally transforming legacy control environments, this hybrid expertise will become indispensable. The competition to hire and retain these specialists will intensify, reshaping security teams and budgets.
Legacy OT Will Become a High-Value Target Adversaries Can No Longer Ignore
As we enter 2026, legacy OT will no longer simply be “outdated technology”. It will become an increasingly vulnerable attack surface that adversaries actively prioritize. Nation-state groups and advanced ransomware operations are already demonstrating a shift toward exploiting unmodernized facilities, slow upgrade cycles, and inconsistent patching across geographically dispersed sites.
These environments often operate under constraints that make modernization difficult. Production uptime is paramount, downtime is expensive, and equipment lifecycles can exceed thirty years. The problem? Adversaries do not operate on these same timelines. In 2026, we will see threat actors focus more energy on smaller, seemingly low-impact facilities whose compromise could trigger regional outages, supply chain disruptions, and cascading failures across national infrastructure systems.
This reality will push policymakers and industry leaders toward bolder actions. Expect increasing emphasis on �secure by design,’ tighter rules for monitoring and managing vulnerabilities, and mandatory patching for high-risk industrial systems. While digital transformation may be expensive and time-consuming, ignoring legacy OT risk will become far more costly.
Kinetic Warfare Will Continue to Drive Innovation in Critical Infrastructure Security
Conflict over the past several years has made one fact clear. Cyber and physical warfare are no longer separate domains, they are deeply intertwined. When Russia invaded Ukraine in 2014 and again in 2022, there was a noticeable disconnect between physical operations and cyberattacks on infrastructure. In 2025, that gap nearly disappeared. Malware was deployed against substations, communication systems, and logistics hubs in near real time as physical operations advanced. Digital operations became the opening act.
In 2026, this alignment will accelerate. Modern militaries now treat cyber operations as an integral part of battlefield planning, and critical infrastructure is squarely in the crosshairs. Electric grids, pipelines, rail systems, maritime ports, and water facilities will face heightened pressure to improve resilience, redundancy, and response capabilities. Operators will need clearer threat intelligence, stronger segmentation, more mature detection programs, and rapid coordination across federal, state, and private sector partners.
This trend will also influence technological innovation. Expect continued investment in anomaly detection for industrial processes, more realistic cyber-physical training exercises, and defensible architectures that assume adversaries are already inside your network.
Looking Ahead
2026 will force organizations to confront uncomfortable but necessary realities about the fragility and importance of their cyber-physical systems. The workforce will change, the threat landscape will intensify, and the intersection of cyber and kinetic conflict will redefine security expectations. Organizations that act now will enter the year with an advantage. Those that wait will find themselves reacting to threats that have already passed their defenses.
##
ABOUT THE AUTHOR
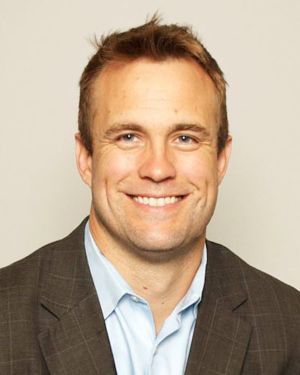
Sean Tufts brings a powerful blend of deep industrial cybersecurity expertise, go-to-market leadership, and a passion for securing the world’s most critical infrastructure. With a career that spans leading roles at GE and Optiv, he has been a driving force in helping asset-intensive industries navigate the intersection of OT, IT, and cyber risk management. Before entering the world of cybersecurity, Sean was a standout linebacker and team captain for the University of Colorado. Sean was a 6th round pick to the Carolina Panthers, spending 3 years running down on kick-offs. That same competitive drive and leadership mindset have shaped his approach to his work in cyber. As Field CTO at Claroty, Sean works closely with customers, partners, and internal teams to drive technical strategy, elevate field execution, and ensure Claroty’s platform continues to deliver tangible outcomes that matter most.