By Brian Wald, Head of Global Field CTO org at GitLab
Every week brings a new model, agent, or tool promising productivity gains that nobody can measure consistently yet. For CIOs, the decisions compound faster than the answers. Which tools get approved? Who owns the workflow when three teams pick three different agents? And how do you make those decisions when the field may look entirely different in three months?
Two distinct paths are emerging in response to this challenge. Startups and small teams optimize for speed and agility, rapidly adopting whichever tools promise the fastest time to market. Meanwhile, enterprises prioritize constraints like data privacy, sovereignty, and compliance, which are fundamental to their operations.
This tension creates a dilemma. The pace of AI advancement means entirely new capabilities will constantly emerge. You can’t keep changing your entire stack every few months, but standing still means falling behind competitors who are moving faster.
The Real Bottleneck Is Tool Fragmentation
The bottleneck isn’t a lack of AI capabilities. The problem is too many tools and not enough control.
Recent data shows that 60% of development teams use more than five different tools for software development, and 49% use more than five AI tools. The impact of this fragmentation carries a steep price. DevSecOps professionals lose seven hours per week to inefficiencies, amounting to nearly an entire workday spent navigating disconnected workflows, chasing approvals across systems, and switching context between platforms.
You might think the solution is to restrict tool adoption, to mandate a single approved stack. But this approach breaks down when it meets reality. Developers will use the tools they want. Shadow IT has transformed into shadow AI, and restriction just pushes adoption underground. The question is whether you govern and orchestrate the workflow or pretend the fragmentation isn’t happening.
From Vibe Coding to Enterprise-Grade Results
Anyone can now prompt their way to functional code, translating business requirements into working applications through natural language. This accessibility represents real progress, but 73% of organizations have already experienced significant problems with the “vibe coding” approach.
The non-deterministic nature of LLMs means the same prompt can generate different outputs, producing validation challenges that didn’t exist with traditional development tools. AI can refine the solution it receives, but only humans can step back and assess whether teams are solving the right problem the right way.
Enterprise development runs on pre-existing codebases spanning millions of lines, non-negotiable compliance requirements, legacy system integrations, and complex security protocols. These constraints can make AI less effective and make AI output harder to trust, review, and audit. A seemingly minor change in one line of code can ripple through interconnected systems in ways that even experienced developers struggle to predict without comprehensive context.
AI helps developers write exponentially more code, which means more reviews, more tests to run, more surface area to protect, and more technical debt to manage. This is the scale trap. AI accelerates one part of the development lifecycle while creating bottlenecks everywhere else. The result is longer review queues, slower test cycles, and security scan backlogs that never shrink. As code complexity grows, the speed, agility, and accuracy that made AI attractive begin to erode, pushing teams into a cycle where they move faster only to slow down.
The Platform as Air Traffic Control
The governance crisis is intensifying. Seventy percent of organizations report that AI makes compliance management more challenging, not easier. Individual tools can’t solve this because each tool only sees its own slice, and there is no single point solution that has visibility across the entire software development lifecycle.
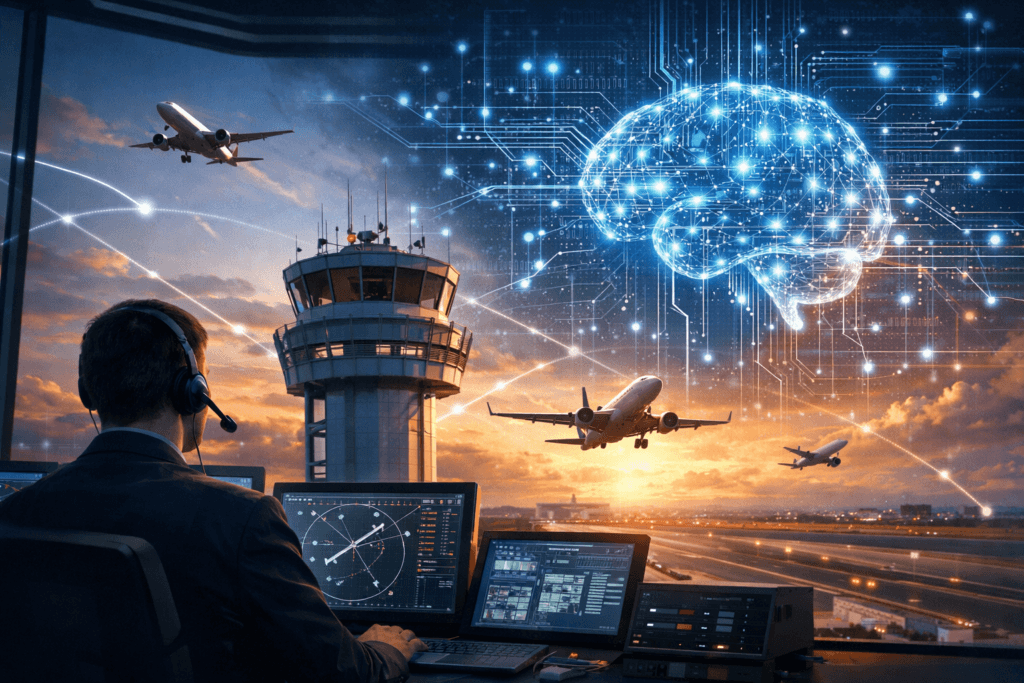
The pattern is predictable as it is one we have seen in DevSecOps long before AI. Point solutions, no matter how sophisticated, can’t address the interconnected requirements of AI orchestration, governance, and compliance. Organizations need a platform that acts as air traffic control, ensuring every vehicle follows the rules while still allowing drivers to choose their preferred route.
A platform orchestration approach delivers this in practice:
- Single Point of Control: Every piece of code, regardless of which AI tool generated it, moves through a unified platform that applies your organization’s rules and regulations consistently.
- Comprehensive Context: The platform equips AI agents with project plans, test suites, compliance checks, security scans, and the dependency graph they need to operate safely across your SDLC. With this context, agents generate plausible code that breaks downstream, and nobody catches it until production.
- Validated Outputs at Scale: Non-deterministic AI outputs require consistent quality checks. A platform approach systematically runs these validation loops, catching issues before they compound into production problems.
- Data Privacy by Design: The platform meets enterprise-level data sovereignty requirements so your code and intellectual property remain under your control, not feeding someone else’s training models.
- Provider-Agnostic Developer Freedom within Guardrails: Developers can use their preferred tools and experiment with emerging technologies, while the platform ensures everything meets enterprise standards. The test: if you swap a model provider next quarter, does the workflow survive, or does every team start over?
Building a Foundation for Constant Change
Organizations that build orchestration infrastructure today gain the ability to adopt new tools without rewriting governance every time. As AI capabilities evolve, they can integrate new models and agents immediately while competitors work to retrofit governance into fragmented toolchains.
Developers gain the freedom to innovate with their preferred tools, to experiment with emerging capabilities, and to solve problems using whatever approaches work best. The enterprise gains confidence that the platform enforces security protocols, meets compliance requirements, and maintains consistent code quality regardless of origin.
Every enterprise needs air traffic control for its AI development landscape. The question is whether leaders implement that control through a platform approach that supports innovation, or through restrictions that push development underground into shadow AI.
The enterprises that will lead the next era are those that enable developer creativity within clear guardrails and treat platform engineering as product work, with owners, roadmaps, and feedback loops, not as a procurement decision. That’s the difference between a foundation that compounds and a program that stalls.
##
ABOUT THE AUTHOR
Brian Wald is Head of Global Field CTO org at GitLab. He
leads a dynamic team of Field CTOs dedicated to transforming enterprise
software development practices.