Industry executives and experts share their predictions for 2022. Read them in this 14th annual VMblog.com series exclusive.
The Supply Chain’s Broken Link
By Paul Ayers, CEO and Co-Founder, Noetic Cyber
In recent years, supply chain vulnerabilities have been a massive issue. In 2020 and 2021, we witnessed the SolarWinds and Kaseya attacks that shined a light on the importance of cybersecurity with respect to the business supply chain. These attacks left several individuals questioning how to manage cyber assets to find and fix security gaps. To provide further insight, below are three critical trends in the area of cybercrime and actions needed to prevent cybercriminals from exploiting your organization’s data.
Supply chain cyber attacks will persist
What we are witnessing currently in the cyber industry is part of a dynamic process. In 2020 and 2021, the cybersecurity industry witnessed a shift in focus to supply chain security, with large supply chain attacks such as SolarWinds and Kaseya. Additionally, large-scale cloud vulnerabilities, such as the recent ChaosDB case are also a cause for concern. From greater than 50 new vulnerabilities per day in 2020, there is no reason to believe that 2021 saw a decrease. The catalog published by CISA on known and exploitable vulnerabilities is very helpful, but the challenge of fighting to secure these vulnerabilities remains. Patching is hard, and prioritization is key. Looking ahead to 2022, it is evident that supply chain attacks will remain a huge threat and difficult for security teams to anticipate. For that reason, security teams must be able to map vulnerabilities to assets, business-critical applications and potential risk.
The cyber industry will see renewed focus on prevention vs. response
Spotting a problem before it becomes a problem is the best way to defend against cyber attacks. Supply chain attacks will continue to be a huge threat to organizations, and difficult for individual security teams to anticipate. The cyber industry swings back and forth between prevention and response, with a renewed focus on preventative approaches, such as security posture management, cyber hygiene and cyber asset management, showing that organizations are trying to anticipate cybersecurity threats before the threat becomes an attack.
Cyber cartography will take center-stage
A more holistic approach to cyber-risk analysis is essential to improving cybersecurity. We continue to face the same problem we have seen for many years: we have too many single-use cyber tools. Forward-thinking security teams are investing in data scientists and working to unlock this siloed telemetry and generate a wider cybersecurity view of the organization to build an advantage over attackers. Phil Venables, the CISO at Google Cloud, has discussed ‘cyber cartography’ as the way of mapping cyber risk, assets, vulnerabilities, users and more in an effort to gain this advantage. To change the status quo in 2022, organizations must employ this proactive approach to ensure they are one step ahead of the adversary at all times.
The threat landscape will continue to evolve in 2022 with continued pressure on known vulnerabilities within the supply chain. It is critical that security teams work together to build a better view of the organization than the attacker. This approach will assist in changing the status quo in 2022 and allowing organizations to take back control of what is rightfully theirs.
##
ABOUT THE AUTHOR
Paul Ayers, CEO and Co-Founder, Noetic Cyber
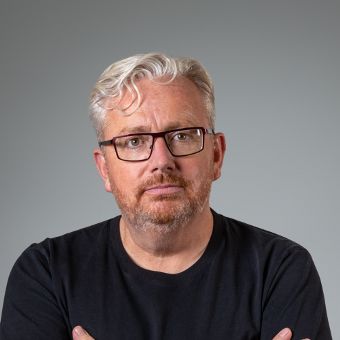
Paul Ayers is a co-founder and Chief Executive Officer at Noetic Cyber. He has a 30-year proven track record of building successful cybersecurity companies in a series of leadership roles across 5 start-ups, all with successful exits. Before founding Noetic in 2019, Paul was an Entrepreneur in Residence (EIR) at TenEleven Ventures, responsible for finding and developing innovative cybersecurity startups.